MARKATA FIELD NOTES THE OPEN WEB
Pins
A field notebook of saved links
911collected links
Saved linksLast filed 2026-10-02
linux - What is stored in /dev/pts files and can we open them?…
Note today I learned that /dev/pts is a pseudo-tty. It amazes me how much linux is still built around things like hardware terminals.
today I learned that /dev/pts is a pseudo-tty. It amazes me how much linux is still built around things like hardware terminals.
svenstaro/miniserve: 🌟 For when you really just want to serve …
Note miniserve is a sweet http server, replacement for python -m http.server. It’s fast, runs off a small binary, but why would I want to use it over something that already exists on most machines, because it includes a bunch of features like qr codes, pretty themes, and uploads. I’ve used python -m http.server many times to transfer files from one machine to another in a pinch, like at a family members house. But what if they have an android, windows, or something not easy to get a python repl running on, you can run miniserve and upload from their device rather than hosting from their device.
miniserve is a sweet http server, replacement for python -m http.server. It’s fast, runs off a small binary, but why would I want to use it over something that already exists on most machines, because it includes a bunch of features like qr codes, pretty themes, and uploads. I’ve used python -m http.server many times to transfer files from one machine to another in a pinch, like at a family members house. But what if they have an android, windows, or something not easy to get a python repl running on, you can run miniserve and upload from their device rather than hosting from their device.
pacman/Tips and tricks - ArchWiki
Note The arch wiki is always full of good content, and pacman tips and tricks does not disappoint. Today I discovered this command to remove orphaned dependencies on my system.
The arch wiki is always full of good content, and pacman tips and tricks does not disappoint. Today I discovered this command to remove orphaned dependencies on my system.
Inside 22,734 Steam games | daniel.haxx.se
Note Interesting to see that curl is used in so many places. I often think of things like games being so windows centric and curl being so linux centric I don’t even think of these things crossing paths as much as they do.
Interesting to see that curl is used in so many places. I often think of things like games being so windows centric and curl being so linux centric I don’t even think of these things crossing paths as much as they do.

wcurl is here | daniel.haxx.se
Note interesting, seems like such a simple way to completely remove the need of a whole other cli. No offense to anyone working on wget, but generally I use it out of lazyness or something wierd is happening and I am looking for a second opinion. Cool to know that wcurl exists and will start shipping with curl.
interesting, seems like such a simple way to completely remove the need of a whole other cli. No offense to anyone working on wget, but generally I use it out of lazyness or something wierd is happening and I am looking for a second opinion. Cool to know that wcurl exists and will start shipping with curl.

Email Address Obfuscation · Cloudflare Web Application Firewal…
Note I recently started seeing email-decode.min.js show up on my blog posts, and I wondered what the heck ? I didn’t put it there. Turns out that cloudflare put it there from pages to safely serve email addresses for me. inspecting the page without js running we can see that the mailto email is swapped out for email protected. Neat feature. Looking deeper into this article it looks like this feature comes from Scrape Shield and enabling Email Address Obfuscation.
I recently started seeing email-decode.min.js show up on my blog posts, and I wondered what the heck ? I didn’t put it there. Turns out that cloudflare put it there from pages to safely serve email addresses for me.
inspecting the page without js running we can see that the mailto email is swapped out for email protected. Neat feature.
Looking deeper into this article it looks like this feature comes from Scrape Shield and enabling Email Address Obfuscation.
Background Tasks - FastAPI
Note fastapi comes with a concept of background tasks which are functions that can be ran in the background after a function has been ran. This is handy for longer running functions that may take some time and you want to have fast response times. Here is an example from the docs
fastapi comes with a concept of background tasks which are functions that can be ran in the background after a function has been ran. This is handy for longer running functions that may take some time and you want to have fast response times.
Here is an example from the docs
markdown-it-pyrs · PyPI
Note markdown it py running in rust claims to be 20x faster. I’ll definitely look into this if markdown it py is ever a bottleneck in my performance. At first glance it appears that plugins are written in rust not python, and there is no admonition plugin, so I’ll keep my eye on it for now, but I can’t use it.
markdown it py running in rust claims to be 20x faster. I’ll definitely look into this if markdown it py is ever a bottleneck in my performance. At first glance it appears that plugins are written in rust not python, and there is no admonition plugin, so I’ll keep my eye on it for now, but I can’t use it.
DiskCache API Reference — DiskCache 5.6.1 documentation
Note diskcache has a peekitem method that allows you to lookup the expire_time of a cached item without changing it. I recently used this to implement debounce for fastapi background tasks with multiple workers running. since all the workers I care about are on the same machine, but running in different processes diskcache was a great option. All workers have access to the same disk, but not the same variables in memory.
diskcache has a peekitem method that allows you to lookup the expire_time of a cached item without changing it. I recently used this to implement debounce for fastapi background tasks with multiple workers running. since all the workers I care about are on the same machine, but running in different processes diskcache was a great option. All workers have access to the same disk, but not the same variables in memory.

Kustomize: The Best Way to Manage Your Kubernetes Configs - Yo…
Note Great intro into kustomize. This helped me get started with kustomize.
Great intro into kustomize. This helped me get started with kustomize.
Alternatives · joric/nrfmicro Wiki
Note Huge list of micro controllers tried and used in keeb builds.
Huge list of micro controllers tried and used in keeb builds.

Waylon Walker - handwired macropads on X: “First bit of hand w…
Note Not gonna lie, kinda pumped about this one. I manually did one, jotted down the coordinates, opened the gcode in vim, added markers between setup/teardown and print. then added the wipe, the copy pasted the print+wipe section a bunch of times. My printer tends to run a bit better on single prints than printing a dozen at once as it has less issues with retract start and stop.
Not gonna lie, kinda pumped about this one. I manually did one, jotted down the coordinates, opened the gcode in vim, added markers between setup/teardown and print. then added the wipe, the copy pasted the print+wipe section a bunch of times.
My printer tends to run a bit better on single prints than printing a dozen at once as it has less issues with retract start and stop.

Find And Replace one eyed kirby
Note another great use and demo of the one eyed fighting kirby
another great use and demo of the one eyed fighting kirby
PolyFill Vulnerability is WILD - YouTube
Note Damn, supply chain vector attacks are wild. Random guy in Primes stream was getting $40k offers to buy their open source project while in university and they have never made anything from it. What a social engineering attack this is. It would be so easy to make it look like a good deal and that the package was going to a good new owner who has real resources to maintain it.
Damn, supply chain vector attacks are wild. Random guy in Primes stream was getting $40k offers to buy their open source project while in university and they have never made anything from it. What a social engineering attack this is. It would be so easy to make it look like a good deal and that the package was going to a good new owner who has real resources to maintain it.

Found: OverlayKey X – Thomas Baart’s Microblog
Note This is almost exactly what I have been thinking about building for quite awhile. I am going to give it a good try with a few $$ in filiment some cheap switches a microcontroller and go pretty bare bones, maybe open wiring on the bottom.
This is almost exactly what I have been thinking about building for quite awhile. I am going to give it a good try with a few $$ in filiment some cheap switches a microcontroller and go pretty bare bones, maybe open wiring on the bottom.
Queueing – An interactive study of queueing strategies – Encor…
Note Absolutely sick post. This is top tier animated blog posts. This posts demos how different queuing systems work with fantastic interactive demos.
Absolutely sick post. This is top tier animated blog posts. This posts demos how different queuing systems work with fantastic interactive demos.

One Script Tag Just Pwn’d Over 100,000 Websites - YouTube
Note Supply chain attacks are so big these days engineers definitely need to take these into consideration. It’s wild that such a simple attack vector hit some really big applications. This particular vector is so easy to avoid. You are already hosting web content, just curl the file and self host the script, then you own it. That eliminates this attack vector all together, but doesn’t completely remove supply chain attacks, the js file can still hit external apis internally. What I see has happened in this case is that the owner of the domain polyfill.io changed. so anyone who directly linked to them got a malware injected script used. I can only imagine the number of applicatons that are not even being maintained anymore getting hit by this. TLDR, if you are taking something to production, where you are goind to deploy it and let it run, host the js yourself. these cdns are great for prototyping, but tread with caution.
Supply chain attacks are so big these days engineers definitely need to take these into consideration. It’s wild that such a simple attack vector hit some really big applications. This particular vector is so easy to avoid. You are already hosting web content, just curl the file and self host the script, then you own it. That eliminates this attack vector all together, but doesn’t completely remove supply chain attacks, the js file can still hit external apis internally.
What I see has happened in this case is that the owner of the domain polyfill.io changed. so anyone who directly linked to them got a malware injected script used.
I can only imagine the number of applicatons that are not even being maintained anymore getting hit by this. TLDR, if you are taking something to production, where you are goind to deploy it and let it run, host the js yourself. these cdns are great for prototyping, but tread with caution.
Don’t Cheat Yourself - YouTube
Note Well spoken prime. Co-pilot is a fantastic tool for templating, boilerplate, or just getting something done that is just outside your knowledge or care to know. Bit if you really want to learn something, you need to use your hands. Reading the solution only gives you the happy path. This does not give you that path that most people would take, and completely misses debugging. If you are very new and learning it’s unlikely that you can write large blocks of code without running a test or a script to try it. Taking these shortcuts will hinder your ability to do it yourself. If I were to devils advocate here, copilot is still not the greatest at the big picture, you still have to drive, and tell it I want to use python, fastapi, I want to load settings from .env. taking these shortcuts can help you move quick and get the big picture. This is especially helpful for someone who might know one language or framework and is trying a different one, but at some point you need to do the work and learn if you are going to be effective.
Well spoken prime. Co-pilot is a fantastic tool for templating, boilerplate, or just getting something done that is just outside your knowledge or care to know. Bit if you really want to learn something, you need to use your hands. Reading the solution only gives you the happy path. This does not give you that path that most people would take, and completely misses debugging. If you are very new and learning it’s unlikely that you can write large blocks of code without running a test or a script to try it. Taking these shortcuts will hinder your ability to do it yourself.
If I were to devils advocate here, copilot is still not the greatest at the big picture, you still have to drive, and tell it I want to use python, fastapi, I want to load settings from .env. taking these shortcuts can help you move quick and get the big picture. This is especially helpful for someone who might know one language or framework and is trying a different one, but at some point you need to do the work and learn if you are going to be effective.
PyAnnotate: Auto-generate PEP-484 annotations
Note pyannotate is a tool that uses runtime types to suggest type annotations to use. Test runners such as pytest can be used to generate the types.
pyannotate is a tool that uses runtime types to suggest type annotations to use. Test runners such as pytest can be used to generate the types.
qmk_firmware/docs/features/programmable_button.md at master · …
Note Interesting, linux supports 32 programmable buttons, special buttons that do nothing that hotkey programs like xbindkeys can pick up and run things, seems like it would be very intersting to use on a macro pad. You could easily do dynamic and complex tasks without clashing that keybinding with something else. I’m going to look into this for my next obs setup. No matter what I try to do with the hyper key it always tends to do odd things depending on the application I am in. typically its tmux, and it starts trying to do something I don’t want it to.
Interesting, linux supports 32 programmable buttons, special buttons that do nothing that hotkey programs like xbindkeys can pick up and run things, seems like it would be very intersting to use on a macro pad. You could easily do dynamic and complex tasks without clashing that keybinding with something else.
I’m going to look into this for my next obs setup. No matter what I try to do with the hyper key it always tends to do odd things depending on the application I am in. typically its tmux, and it starts trying to do something I don’t want it to.
tusharsadhwani/yen: Create virtual environments for any Python…
Note Create virtual environments for any Python version, without needing Python installed.
Create virtual environments for any Python version, without needing Python installed.
Where DOESN’T curl run with curl BDFL Daniel Stenberg (Changel…
Note Love how Daniel just brushed off the number of netflix tv installs as small beans for curl installs. overall great episode on open source, owning a major component to technology with such a small team.
Love how Daniel just brushed off the number of netflix tv installs as small beans for curl installs. overall great episode on open source, owning a major component to technology with such a small team.
Keyboard Mounting Styles — Keyboard University
Note Great keyboard design guide for all the different mounting options that are normal for keyboards with pros and cons of each.
Great keyboard design guide for all the different mounting options that are normal for keyboards with pros and cons of each.
Welcome to RSS Club - daverupert.com
Note Super cool idea, kinda breaking the rules by talking about it here, but Its a cool idea to throw out posts to the core audience. Apparently its been around for quite while Dave started in 2018.
Super cool idea, kinda breaking the rules by talking about it here, but Its a cool idea to throw out posts to the core audience. Apparently its been around for quite while Dave started in 2018.
Releases · stackrox/kube-linter
Note A linter for linting kubernetes manifests and help charts.
A linter for linting kubernetes manifests and help charts.
Keycodes Overview | QMK Firmware
Note Full reference to all of the qmk keycode list. Handy reference to refer to all of the keycodes that qmk has.
Full reference to all of the qmk keycode list. Handy reference to refer to all of the keycodes that qmk has.
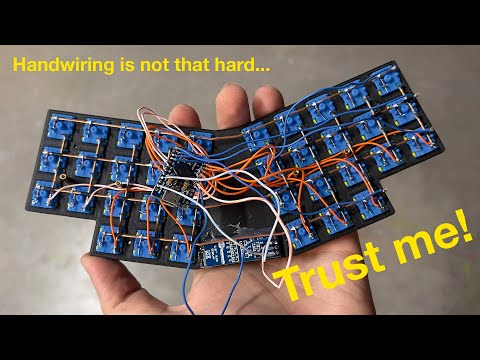
How to Build a Handwired Keyboard - YouTube
Note Fantastic guide to building handwried keyboards. I used this guide to build my first hand-wired macro pad.
Fantastic guide to building handwried keyboards. I used this guide to build my first hand-wired macro pad.

Adam Wathan, Creator of TailwindCSS - YouTube
Note Two inspirational people in one podcast, its cool to see how adam thinks about code, css, webdev, and building businesses.
Two inspirational people in one podcast, its cool to see how adam thinks about code, css, webdev, and building businesses.
Episode #323 Best practices for Docker in production - [Talk P…
Note Great listen for anyone interested in productionizing python code with docker. Itamar brings up some Don’t trust base images for security, upgrade your packages. Vulnerabilties become published and solved giving the bad guys istructions how to wreck your day and these fixes wont come to your docker application for up to two weeks due to image build tatency. For job based containers pre-compile your pyc for faster startup. Alpine linux is probably not what you want for python. Many packages such as postgres ship pre-copiled binaries that work for most linux distributions wich use glibc, but alpine uses musl so the binaries will be incompatable requiring you to need to install a bunch of build dependencies.
Great listen for anyone interested in productionizing python code with docker. Itamar brings up some
Don’t trust base images for security, upgrade your packages. Vulnerabilties become published and solved giving the bad guys istructions how to wreck your day and these fixes wont come to your docker application for up to two weeks due to image build tatency.
For job based containers pre-compile your pyc for faster startup.
Alpine linux is probably not what you want for python. Many packages such as postgres ship pre-copiled binaries that work for most linux distributions wich use glibc, but alpine uses musl so the binaries will be incompatable requiring you to need to install a bunch of build dependencies.

Why You Should Build Your Homelab Now - YouTube
Note Homelabbers have been some of the best co-workers I have ever had. Typically have a get shit done, If there’s a way I will find it kind of mentality. If you are struggling to get a job in tech right now its tough. Starting a homelab on a pc you pull out of the trash is a good way to get some experience that you can talk about in interview questions. Linked video has some great points!
Homelabbers have been some of the best co-workers I have ever had. Typically have a get shit done, If there’s a way I will find it kind of mentality. If you are struggling to get a job in tech right now its tough. Starting a homelab on a pc you pull out of the trash is a good way to get some experience that you can talk about in interview questions.
Linked video has some great points!
podman requries qemu-system on ubuntu
Note podman requires qemu-system on The fix to this for me was to install qemu-system before podman machine init.
podman requires qemu-system on
The fix to this for me was to install qemu-system before podman machine init.
Customize and apply backgrounds fast | SVG Backgrounds
Note svgbackgrounds is a really awesome resource for svg things recently featured on https://shoptalkshow.com/618/
svgbackgrounds is a really awesome resource for svg things recently featured on https://shoptalkshow.com/618/
darrenburns/posting: Test your HTTP API using a powerful and m…
Note Currently Posting is a super early postman like tui (terminal user interface). It looks so good. Darren is really getting into a groove, and textual is getting to a place that is allowing him to really make these beautiful. I am so impressed with the progress that he has made so early, it looks so close to postman in the freaking terminal, and the ui is so good. He already has think like jump that give you a way to around the ui like easymotion plugins. Theres themes and a command line, oh man its so good. star it.
Currently Posting is a super early postman like tui (terminal user interface). It looks so good. Darren is really getting into a groove, and textual is getting to a place that is allowing him to really make these beautiful.
I am so impressed with the progress that he has made so early, it looks so close to postman in the freaking terminal, and the ui is so good. He already has think like jump that give you a way to around the ui like easymotion plugins. Theres themes and a command line, oh man its so good. star it.
Blogmarks that use markdown
Note Oh I kinda like the name blogmark, as opposed to thoughts like I have chose for the same thing. Aparantly Simon beat me to the punch by 20 years on this one.
Oh I kinda like the name blogmark, as opposed to thoughts like I have chose for the same thing. Aparantly Simon beat me to the punch by 20 years on this one.
A Link Blog in the Year 2024
Note THIS! is the same reasons that I built thoughts{.hoverlink}. Simon has bee a big inspiration along the way. He defintely changed the format of my posts as I watched him build out his quote posts. Link blogging is a pleasantly low-pressure way of writing online. Found something interesting? Post a link to it, with a sentence or two about why it’s worth checking out. Ditto! just make a post.
THIS! is the same reasons that I built thoughts{.hoverlink}. Simon has bee a big inspiration along the way. He defintely changed the format of my posts as I watched him build out his quote posts.
Link blogging is a pleasantly low-pressure way of writing online. Found something interesting? Post a link to it, with a sentence or two about why it’s worth checking out.
Ditto! just make a post.
A Link Blog in the Year 2024 | Kellan Elliott-McCrea: Blog
Note Kellan brings some interesting thoughts on where the internet is headed in 2024. Interestingly I see myself headed in a similar direction. Feeling like I know just enough to say fuck it and build my own platform for me to me me, from thoughts{.hoverlink} where I link and make thoughts on posts like this, to reader{.hoverlink} which is my rss reader replacement that I wanted in 2013 when it was killedbygoogle And particular with the collapse of the social spaces many of us grew up with, I feel called back to earlier forms of the Internet, like blogs, and in particular, starting a link blog. Ai has really had quite the two sided effect since chatgpt launched and set the world ablaze. Suddenly you can get any answer you want as a custom fit blog post for free without effort, thus killing the traffic to any of these sites.
Kellan brings some interesting thoughts on where the internet is headed in 2024. Interestingly I see myself headed in a similar direction. Feeling like I know just enough to say fuck it and build my own platform for me to me me, from thoughts{.hoverlink} where I link and make thoughts on posts like this, to reader{.hoverlink} which is my rss reader replacement that I wanted in 2013 when it was killedbygoogle
And particular with the collapse of the social spaces many of us grew up with, I feel called back to earlier forms of the Internet, like blogs, and in particular, starting a link blog.
Ai has really had quite the two sided effect since chatgpt launched and set the world ablaze. Suddenly you can get any answer you want as a custom fit blog post for free without effort, thus killing the traffic to any of these sites.

How to Configure DNS over TLS (DoT) Using Unbound DNS in OPNsense
Note Setting up DNS overTLS in opnsense has made my dns just a bit more secure and reliable. I recently had an outage of half the internet within my house. This also hit some of my friends and not some. It did not hit my mobile network. What seems to have happened is a dns issue with my isp not resolving some domains. This setup corrected my issue and I was back online more securely. Note I did try to setup the family resolver and found it was blocking some sites I am ok with. I decided to drop back to the vanilla resolver and let other services within opnsense control blocking where I can caontrol the whitelist myself.
Setting up DNS overTLS in opnsense has made my dns just a bit more secure and reliable. I recently had an outage of half the internet within my house. This also hit some of my friends and not some. It did not hit my mobile network. What seems to have happened is a dns issue with my isp not resolving some domains. This setup corrected my issue and I was back online more securely.
Note
I did try to setup the family resolver and found it was blocking some sites I am ok with. I decided to drop back to the vanilla resolver and let other services within opnsense control blocking where I can caontrol the whitelist myself.
argoproj/argo-events: Event-driven Automation Framework for Ku…
Note Argo events is an event driven automation framework for kubernetes that can create kubernetes objects among other things based on events. I’ve been using native kubernetes cronjobs to kick off jobs based on a cron trigger. For instance I am running reader.waylonwalker.com every hour, to rebuild the site and re-deploy it. It takes about two minutes to fetch every rss feed, so this is a nice application of a job compared to a web server fetching the feeds live. Now my posts may be up to an hour stale but they load fast. Argo events takes event drien architecture to the next level allowing to be triggered by many more things, and do many more things than creating a cron job. I’m definitely thinking about dropping this in my homelab.
Argo events is an event driven automation framework for kubernetes that can create kubernetes objects among other things based on events. I’ve been using native kubernetes cronjobs to kick off jobs based on a cron trigger.
For instance I am running reader.waylonwalker.com every hour, to rebuild the site and re-deploy it. It takes about two minutes to fetch every rss feed, so this is a nice application of a job compared to a web server fetching the feeds live. Now my posts may be up to an hour stale but they load fast.
Argo events takes event drien architecture to the next level allowing to be triggered by many more things, and do many more things than creating a cron job. I’m definitely thinking about dropping this in my homelab.
catppuccin/ulauncher: 🇺 Soothing pastel theme for Ulauncher
Note I am using this theme for Ulauncher in arch and it looks fantastic! One line install (read it first).
I am using this theme for Ulauncher in arch and it looks fantastic! One line install (read it first).
Ulauncher — Application launcher for Linux 🐧
Note Just discovered this really cool launcher from the DHH distro omakub. github.com/omakub{.hoverlink}. Ulauncher comes out of the box looking good, supports extensions, and shortcuts like I have a lot of mac launchers have. I installed it plus a theme and in no time It was looking good and launching applications. In the past I have leaned in on rofi for task launching, it is good. I just felt it was harder to configure to get right or look good.
Just discovered this really cool launcher from the DHH distro omakub. github.com/omakub{.hoverlink}.
Ulauncher comes out of the box looking good, supports extensions, and shortcuts like I have a lot of mac launchers have. I installed it plus a theme and in no time It was looking good and launching applications.
In the past I have leaned in on rofi for task launching, it is good. I just felt it was harder to configure to get right or look good.
Steam Deck dock
Note This is a sick steam deck dock! With a corne built in laptop style.
This is a sick steam deck dock! With a corne built in laptop style.
basecamp/omakub: Opinionated Ubuntu Setup
Note This is DHH’s linux startup script. Call it a distro if you want, but he doesn’t. It’s made to take a vanilla ubuntu install and configure everything the way he likes it. There’s a number of great nuggets in here to pick up on. No need to write bespoke configs for every essential tool just to get started or to be up on all the latest command-line tools. Omakub is an opinionated take on what Linux can be at its best. Check it out and give it a ⭐ basecamp/omakub{.hoverlink}.
This is DHH’s linux startup script. Call it a distro if you want, but he doesn’t. It’s made to take a vanilla ubuntu install and configure everything the way he likes it. There’s a number of great nuggets in here to pick up on.
No need to write bespoke configs for every essential tool just to get started or to be up on all the latest command-line tools. Omakub is an opinionated take on what Linux can be at its best.
Check it out and give it a ⭐ basecamp/omakub{.hoverlink}.
From the Circle to Epicycles (Part 1) - An animated introducti…
Note This is a really cool animated visual representation of how sine waves work, how they relate to circles, pi, rad, and how to add up a series of waves to make square and sawtooth waves.
This is a really cool animated visual representation of how sine waves work, how they relate to circles, pi, rad, and how to add up a series of waves to make square and sawtooth waves.
Darren Burns 🌱 on X: “Here’s an early clip of my new (work in …
Note This looks like a sweet tui postman clone. Darren is really rolling with these tui’s. Cant wait to see where this one goes.
This looks like a sweet tui postman clone. Darren is really rolling with these tui’s. Cant wait to see where this one goes.
How to Force Dark Mode on Every Website in Google Chrome
Note Sometimes I struggle to get my os to report dark mode to chrome, luckily there is a way to force chrome to always use dark mode. I’ve never really gotten into dark reader and extensions like this. For some reason they all make websites look really weird to me and I don’t really care for it. What I want is websites designed to be in dark/light to always go dark, if the designer didn’t design dark just let it be light.
Sometimes I struggle to get my os to report dark mode to chrome, luckily there is a way to force chrome to always use dark mode.
I’ve never really gotten into dark reader and extensions like this. For some reason they all make websites look really weird to me and I don’t really care for it. What I want is websites designed to be in dark/light to always go dark, if the designer didn’t design dark just let it be light.
xxHash - Extremely fast non-cryptographic hash algorithm
Note xxHash is an extremely fast non-cryptographic hash algorithm, working at RAM speed limit. It is proposed in four flavors (XXH32, XXH64, XXH3_64bits and XXH3_128bits). The latest variant, XXH3, offers improved performance across the board, especially on small data.
xxHash is an extremely fast non-cryptographic hash algorithm, working at RAM speed limit. It is proposed in four flavors (XXH32, XXH64, XXH3_64bits and XXH3_128bits). The latest variant, XXH3, offers improved performance across the board, especially on small data.
xxhash · PyPI
Note I hit an issue with markata where even though a bunch of articles were cached, the site build was still slow because I was hitting hashlib.sha256 so hard for cache keys. I was shocked when this popped up in my profiler as a significant portion of the time spent. I swapped out for xxhash and that issue completely went away.
I hit an issue with markata where even though a bunch of articles were cached, the site build was still slow because I was hitting hashlib.sha256 so hard for cache keys. I was shocked when this popped up in my profiler as a significant portion of the time spent. I swapped out for xxhash and that issue completely went away.
Replicate — Run AI with an API
Note This is so easy compared to self hosting stable diffusion yourself. It even has a nice api that you can hit with curl or python. The pricing seems competitive as well. Bookmarking this to try next time I need something like it.
This is so easy compared to self hosting stable diffusion yourself. It even has a nice api that you can hit with curl or python. The pricing seems competitive as well. Bookmarking this to try next time I need something like it.
How to Deliver Code Every Day | Jake Worth
Note Great set of tips here! No waiting. No “waiting until tomorrow” or “It’s Friday, let’s wait until Monday” to deploy. If your deploys are so slow that deploying an hour before the end of the day is a risk, that’s a separate problem. If you’re afraid of a Friday deploy, your system is too brittle, or you don’t have foolproof rollback procedures, or you don’t have people you trust on call to resolve it. Each of these is a problem that you can fix. This one I find interesting I think there are some industries where customers come in large waves over the weekend, and a weekend bug can not only ruin someones day off, take longer to fix, but also cost a lot of money. Not deploying on Friday is totally what that team should be doing. Most of us are not that team. Most of us work on small teams supporting some sort of product that Should be able to be tested and rolled back. I completely agree with Jake here, if your not willing to deploy on Friday you are not confident in your product. You need to work on better testing, rollback strategies, and feature flagging is what you need. I’ve also been on teams where we don’t deploy in the middle of the day or right before we leave for vacation because we are early, our customers are important to us, and we accept that we have not hit our marks yet on the ability to swiftly recover from some downtime so risk is high.
Great set of tips here!
No waiting. No “waiting until tomorrow” or “It’s Friday, let’s wait until Monday” to deploy. If your deploys are so slow that deploying an hour before the end of the day is a risk, that’s a separate problem. If you’re afraid of a Friday deploy, your system is too brittle, or you don’t have foolproof rollback procedures, or you don’t have people you trust on call to resolve it. Each of these is a problem that you can fix.
This one I find interesting I think there are some industries where customers come in large waves over the weekend, and a weekend bug can not only ruin someones day off, take longer to fix, but also cost a lot of money.
Not deploying on Friday is totally what that team should be doing.
Most of us are not that team. Most of us work on small teams supporting some sort of product that Should be able to be tested and rolled back. I completely agree with Jake here, if your not willing to deploy on Friday you are not confident in your product. You need to work on better testing, rollback strategies, and feature flagging is what you need.
I’ve also been on teams where we don’t deploy in the middle of the day or right before we leave for vacation because we are early, our customers are important to us, and we accept that we have not hit our marks yet on the ability to swiftly recover from some downtime so risk is high.
Be Fast | Jake Worth
Note Be Fast, Practice, Hone your craft. There’s a lot to be said here about honing your craft for editing text, picking up a few extra WPM, learning vim shortcuts. Also just build shit. The more you build new and different things the more not only your text editing will just roll out, your skills to see patterns in code and architecture will flourish. Read their bios, and the answer is always no. They loved to play, sure. They had some base talent, typically. But they also invested an absurd amount of time into that skill set. This! is actually what turned me on to Post Malone. I remember hearing his story in how he was just known as the guy with a guitar because he was always playing it between class and everything.
Be Fast, Practice, Hone your craft. There’s a lot to be said here about honing your craft for editing text, picking up a few extra WPM, learning vim shortcuts.
Also just build shit. The more you build new and different things the more not only your text editing will just roll out, your skills to see patterns in code and architecture will flourish.
Read their bios, and the answer is always no. They loved to play, sure. They had some base talent, typically. But they also invested an absurd amount of time into that skill set.
This! is actually what turned me on to Post Malone. I remember hearing his story in how he was just known as the guy with a guitar because he was always playing it between class and everything.
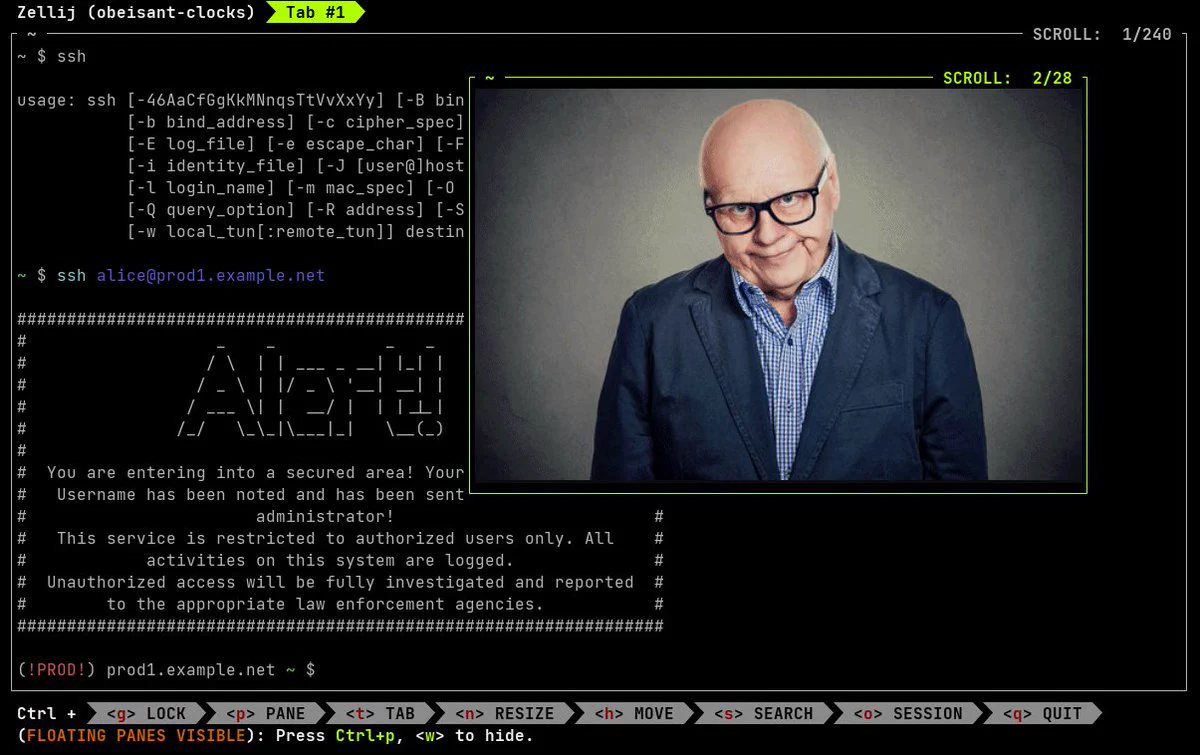
Zellij on X: “POV your sysadmin rigged your terminal to show t…
Note This one is too funny. opening a sixel image in the terminal when logging into prod.
This one is too funny. opening a sixel image in the terminal when logging into prod.
Text Decoration - Tailwind CSS
Note Tailwind calls strikethrough line-through. This caught me off guard and took me a minute to find. Control how text is decorated with the underline, no-underline, and line-through utilities.
Tailwind calls strikethrough line-through. This caught me off guard and took me a minute to find.
Control how text is decorated with the underline, no-underline, and line-through utilities.
Digital Gardening for Non-Technical Folks
Note Maggie is a fantastic proponent to the digital gardening movement. In this article she proposes 3 ways for someone to start their own digital garden with low friction and no code.
Maggie is a fantastic proponent to the digital gardening movement. In this article she proposes 3 ways for someone to start their own digital garden with low friction and no code.
We have a right to repair! with Kyle Wiens, Founder and CEO at…
Note This is one of my favorite changelog episodes of all time. I had no idea all the work that has gone into the right to repair and ifixit. They talk a lot about apple and its trend to be less repairable from unservicable air pods to serialized components within iphone. A lot of legal talk that was far more interesting that I thought it would be. Recently winning the right to repair case against John Deere, and creating repairability scores for devices to be placed in stores like energy guide is.
This is one of my favorite changelog episodes of all time. I had no idea all the work that has gone into the right to repair and ifixit. They talk a lot about apple and its trend to be less repairable from unservicable air pods to serialized components within iphone.
A lot of legal talk that was far more interesting that I thought it would be. Recently winning the right to repair case against John Deere, and creating repairability scores for devices to be placed in stores like energy guide is.

Try Out the Latest Linux Gnome DE With DistroBox
Note Get gnome running in distrobox.
Get gnome running in distrobox.

STLGears.com | The Free STL Gear Designer
Note This is a pretty nice gear generator. I printed a few gears today and it worked great so far.
This is a pretty nice gear generator. I printed a few gears today and it worked great so far.
eraser-dev/eraser: 🧹 Cleaning up images from Kubernetes nodes
Note This is kinda sick, its a tool to clean up container images in a k8s cluster.
This is kinda sick, its a tool to clean up container images in a k8s cluster.

Distrobox
Note distrobox gives you distrobox-host-exec to run commands on the host. This is handy to get access to host level clis that you probably wouldn’t want to run from the container like podman, docker, flatpak. DESCRIPTION distrobox-host-exec lets one execute command on the host, while inside of a container. Under the hood, distrobox-host-exec uses host-spawn a project that lets us execute commands back on the host. If the tool is not found the user will be prompted to install it.
distrobox gives you distrobox-host-exec to run commands on the host. This is handy to get access to host level clis that you probably wouldn’t want to run from the container like podman, docker, flatpak.
DESCRIPTION distrobox-host-exec lets one execute command on the host, while inside of a container.
Under the hood, distrobox-host-exec uses host-spawn a project that lets us execute commands back on the host. If the tool is not found the user will be prompted to install it.
Are We Anti-Cheat Yet?
Note A comprehensive community built index of anti-cheat support for linux very similar to proton, but specific to anticheat support.
A comprehensive community built index of anti-cheat support for linux very similar to proton, but specific to anticheat support.
ublue-os/image-template: Build your own custom Universal Blue …
Note ublue-os makes a github template for making your own git repo with actions that build out your own personal ublue iso.
ublue-os makes a github template for making your own git repo with actions that build out your own personal ublue iso.
ublue-os/obs-studio-portable: OCI container image of OBS Studi…
Note Distrobox is so interesting and cool, I’ve only recently started realizing how much it can do especially related to hardware and graphics, this is quite an example that runs obs in a distrobox. I had no idea distrobox would let you connect to cameras and gpus so seemlessly, and give you a gui to work from. And with distrobox you can export so that it just looks like an app on your system.
Distrobox is so interesting and cool, I’ve only recently started realizing how much it can do especially related to hardware and graphics, this is quite an example that runs obs in a distrobox. I had no idea distrobox would let you connect to cameras and gpus so seemlessly, and give you a gui to work from. And with distrobox you can export so that it just looks like an app on your system.
How Ahrefs Gets a Billion Dollar-Worth Infrastructure With a 9…
Note 2024 has been a wild year for infra with going “back” to on prem being made popular by @dhh. Well it looks like ahrefs saw right through the cloud trends an decided to ride the anti cloud train until it came back around to the station. Being just a bit critical of the article it is impossible to get an apples to apples without actually running something of this scale and spending too much to find out. I cant imagine raw ec2 and ebs being the cheapest route into aws. They used no serverless tech in their article, but I digress, because I like this own your shit and build good product train. What about People?! This follow up does dive into the typical gut reaction that people cost a lot of money, you must account for them. You see when you hire people who are actually good at what they do, and run lean a lot of cost goes away, you have levels of management that disappear, levels of tooling that don’t need to exist, departments of IT don’t need to exist. Colo’s are the new hotness, and will continue to grow! I just notices that they didn’t even account for egress, support and taxes, egress costs would make a difference.
2024 has been a wild year for infra with going “back” to on prem being made popular by @dhh. Well it looks like ahrefs saw right through the cloud trends an decided to ride the anti cloud train until it came back around to the station.
Being just a bit critical of the article it is impossible to get an apples to apples without actually running something of this scale and spending too much to find out. I cant imagine raw ec2 and ebs being the cheapest route into aws. They used no serverless tech in their article, but I digress, because I like this own your shit and build good product train.
What about People?!
This follow up does dive into the typical gut reaction that people cost a lot of money, you must account for them. You see when you hire people who are actually good at what they do, and run lean a lot of cost goes away, you have levels of management that disappear, levels of tooling that don’t need to exist, departments of IT don’t need to exist.
Colo’s are the new hotness, and will continue to grow!
I just notices that they didn’t even account for egress, support and taxes, egress costs would make a difference.
Safer Bash Shebang Recipes - Just Programmer’s Manual
Note When using justfiles each line is ran separately from the last, unless you specify the file to be ran by something other than just such as bash. If you want variables to persist you need to set a shebang. Also if you are using your script i a way that you want it to exit when it fails you need to set -e and -o pipefail. This is critical if you are thinking about using just for production scripts like ci/cd. I’ve hit too bugs where ci passes, but no artifacts were created issues for this exact reason.
When using justfiles each line is ran separately from the last, unless you specify the file to be ran by something other than just such as bash. If you want variables to persist you need to set a shebang.
Also if you are using your script i a way that you want it to exit when it fails you need to set -e and -o pipefail. This is critical if you are thinking about using just for production scripts like ci/cd. I’ve hit too bugs where ci passes, but no artifacts were created issues for this exact reason.

Justfile Cheat Sheet by linux_china - Download free from Cheat…
Note This is a dope ass cheat sheet for justfiles. It’s filled with good examples that are short and to the point, probably all from the docs, but anyways I need to do some like this for myself.
This is a dope ass cheat sheet for justfiles. It’s filled with good examples that are short and to the point, probably all from the docs, but anyways I need to do some like this for myself.
A quote from Tim Paul
Note Damn this Tim Paul quote finishes hard and such a good point. None of the stuff around llms just work. Good ui’s, front end, back end, infrastructure, product. All these things still need to exist, and in fact for ai to be good we need to still go hard on them otherwise everything will die in a heaping pile of ai slop I’m no developer, but I got the AI part working in about an hour. What took longer was the other stuff: identifying the problem, designing and building the UI, setting up the templating, routes and data architecture. It reminded me that, in order to capitalise on the potential of AI technologies, we need to really invest in the other stuff too, especially data infrastructure. It would be ironic, and a huge shame, if AI hype sucked all the investment out of those things. — Tim Paul
Damn this Tim Paul quote finishes hard and such a good point. None of the stuff around llms just work. Good ui’s, front end, back end, infrastructure, product. All these things still need to exist, and in fact for ai to be good we need to still go hard on them otherwise everything will die in a heaping pile of ai slop
I’m no developer, but I got the AI part working in about an hour.
What took longer was the other stuff: identifying the problem, designing and building the UI, setting up the templating, routes and data architecture.
It reminded me that, in order to capitalise on the potential of AI technologies, we need to really invest in the other stuff too, especially data infrastructure.
It would be ironic, and a huge shame, if AI hype sucked all the investment out of those things.
— Tim Paul

PopSQL - Collaborative SQL Editor - Bring Order to SQL Chaos
Note PopSql looks like a very innovative product to bring collaboration to data exploration and visualization in a way you would expect from something like vscode liveshare. This looks far more appealing than a traditional BI data tool.
PopSql looks like a very innovative product to bring collaboration to data exploration and visualization in a way you would expect from something like vscode liveshare. This looks far more appealing than a traditional BI data tool.

Pricing | PopSQL
Note interesting pricing model from popsql (pronounces Popsicle). At a glance you pay for data retention, want the abiltiy to recall all the queries you ran within the last year, run at a higher frequency, you jump a pricing tier.
interesting pricing model from popsql (pronounces Popsicle). At a glance you pay for data retention, want the abiltiy to recall all the queries you ran within the last year, run at a higher frequency, you jump a pricing tier.
Dax Raad - SST, Build modern full-stack applications on AWS wi…
Note such a sick episode with dax. SST’s free tier will be free as long as aws allows a free tier, their free tier literally costs them nothing. They talked about keeping SST small, the limitations that brings, but also the number of problems that just go away when you only have 3 people building. Lots of process disappears, everyone can trust everyone, no one needs to wait for approval, everyone is their own PM and just builds cool shit. They don’t have to worry about big costs and making payroll because they are profitable so much higher than their costs. If they can get through phase one of just being the go platform for a very specific audience of users, and gain marketshare, the ideas of offerings on top of this are endless.
such a sick episode with dax.
SST’s free tier will be free as long as aws allows a free tier, their free tier literally costs them nothing.
They talked about keeping SST small, the limitations that brings, but also the number of problems that just go away when you only have 3 people building. Lots of process disappears, everyone can trust everyone, no one needs to wait for approval, everyone is their own PM and just builds cool shit. They don’t have to worry about big costs and making payroll because they are profitable so much higher than their costs.
If they can get through phase one of just being the go platform for a very specific audience of users, and gain marketshare, the ideas of offerings on top of this are endless.

Install Pokemon TCG Live on Steam Deck - Installation Guide - …
Note I had no idea that you could just drop an msi installer right in steam. This worked for me, and was much easier to install pokemon tcg live in 05-2024 on ubuntu 22-04. I added the msi to steam from my downloads, hit start, failed right away like he said it would. changed compatability to proton experimental, and it opened right up. Download the official installer from pokemon tcg Add non steam game click show all file types navigate to downloaded msi click gear icon > compatability > proton experimental click play profit
I had no idea that you could just drop an msi installer right in steam. This worked for me, and was much easier to install pokemon tcg live in 05-2024 on ubuntu 22-04. I added the msi to steam from my downloads, hit start, failed right away like he said it would. changed compatability to proton experimental, and it opened right up.
Download the official installer from pokemon tcg
Add non steam game
click show all file types
navigate to downloaded msi
click gear icon > compatability > proton experimental
click play
profit

Fields - Pydantic
Note exclude=True and repr=False is a good pydantic combination for secret attributes such as user passwords, or hashed passwords. exclude keeps it out of model_dumps, and repr keeps it out of the logs.
exclude=True and repr=False is a good pydantic combination for secret attributes such as user passwords, or hashed passwords. exclude keeps it out of model_dumps, and repr keeps it out of the logs.
Hatch v1.10.0 - Hatch
Note Hatch be flyin. This new release of hatch includes support for the new package installer uv which is just mind blowing fast compared to anything else we have in python right now. The other features are cool too, check them out. I’ll probably be using the test runner, but I’ve been waiting for the uv support since uv launched.
Hatch be flyin.
This new release of hatch includes support for the new package installer uv which is just mind blowing fast compared to anything else we have in python right now.
The other features are cool too, check them out. I’ll probably be using the test runner, but I’ve been waiting for the uv support since uv launched.
Using journalctl - The Ultimate Guide To Logging
Note I had a boot issue on my sons fresh ubuntu 24.04 install and journalctl came in clutch. -p 3 gives me priority 3 -x gives me extra catalog information when available -b gives me the current boot.
I had a boot issue on my sons fresh ubuntu 24.04 install and journalctl came in clutch.
-p 3 gives me priority 3
-x gives me extra catalog information when available
-b gives me the current boot.

Bug #2006590 “gdm3 crashes with SIGTRAP on startup” : Bugs : g…
Note This Thread saved my son’s ubuntu 24.04 install. His was failing to start with the following error.
This Thread saved my son’s ubuntu 24.04 install. His was failing to start with the following error.
Alir3z4/html2text: Convert HTML to Markdown-formatted text.
Note Super neat tool to convert html to markdown It even plays nicely with rich.
Super neat tool to convert html to markdown
It even plays nicely with rich.

I Interviewed Uncle Bob - YouTube
Note Fantastic interview with Uncle Bob, really it was more of a 2 way conversation. So many of Uncle Bob’s takes have been taken out of context, its cool to hear some of the well actuallys, and the experience behind some of the reasoning.
Fantastic interview with Uncle Bob, really it was more of a 2 way conversation. So many of Uncle Bob’s takes have been taken out of context, its cool to hear some of the well actuallys, and the experience behind some of the reasoning.
How an empty S3 bucket can make your AWS bill explode | by Mac…
Note Imagine waking up to a $1,300 for running an example project! That sounds like peanuts for a cloud bill but for an individual trying to learn that hits my monthly budget real hard. That’s what happened to Marciej, make sure you check out the full article and give them a 👏 on Medium if you have an account. The more I see things come out about aws, the more it makes me sick, and confirm my feelings that I cannot possibly use them for a side project without some real $$ planning to come out of it. Yes, S3 charges for unauthorized requests (4xx) as well[1]. That’s expected behavior. They offer no DDOS protection against 4xx or 5xx requests against your bucket. Absolutely bonkers that you have ZERO control over this. This response just feels absolutely gross. I notified the AWS security team. I suggested that they restrict the unfortunate S3 bucket name to protect their customers from unexpected charges, and to protect the impacted companies from data leaks. But they were unwilling to address misconfigurations of third-party products. It sounds like this guy followed some default instructions for an example site, HOW MANY OTHERS have done this or will do this? And AWS has no response other than to take thier money. After contacting them he was able to get it cancelled, but this is no guarantee. We’ve seen other cloud vendors stick users like this with a few thousand dollar bills after cutting their bill to 5% of the original. AWS was kind enough to cancel my S3 bill. However, they emphasized that this was done as an exception. 2024 is wild on the cloud hosting front, own your shit or be careful.
Imagine waking up to a $1,300 for running an example project! That sounds like peanuts for a cloud bill but for an individual trying to learn that hits my monthly budget real hard.
That’s what happened to Marciej, make sure you check out the full article and give them a 👏 on Medium if you have an account.
The more I see things come out about aws, the more it makes me sick, and confirm my feelings that I cannot possibly use them for a side project without some real $$ planning to come out of it.
Yes, S3 charges for unauthorized requests (4xx) as well[1]. That’s expected behavior.
They offer no DDOS protection against 4xx or 5xx requests against your bucket. Absolutely bonkers that you have ZERO control over this.
This response just feels absolutely gross.
I notified the AWS security team. I suggested that they restrict the unfortunate S3 bucket name to protect their customers from unexpected charges, and to protect the impacted companies from data leaks. But they were unwilling to address misconfigurations of third-party products.
It sounds like this guy followed some default instructions for an example site, HOW MANY OTHERS have done this or will do this? And AWS has no response other than to take thier money.
After contacting them he was able to get it cancelled, but this is no guarantee. We’ve seen other cloud vendors stick users like this with a few thousand dollar bills after cutting their bill to 5% of the original.
AWS was kind enough to cancel my S3 bill. However, they emphasized that this was done as an exception.
2024 is wild on the cloud hosting front, own your shit or be careful.
Media Types
Note A full list of standard Accept types. This is a handy reference.
A full list of standard Accept types.
This is a handy reference.
Network Types - Pydantic
Note pydantic has a nice built in email validator EmailStr It requires an optional pydantic dependency Then you can validate email addresses.
pydantic has a nice built in email validator EmailStr
It requires an optional pydantic dependency
Then you can validate email addresses.
rich.panel — Rich 13.6.0 documentation
Note This is my go to rich response container for clis written in python. It creates a nice box around the content on the screen and provides some nice separation in the output. It can be overdone, but comes in clutch when looking for that print statement in a long output.
This is my go to rich response container for clis written in python. It creates a nice box around the content on the screen and provides some nice separation in the output. It can be overdone, but comes in clutch when looking for that print statement in a long output.
Handling Errors - FastAPI
Note This page shows how to customize your fastapi errors. I found this very useful to setup common templates so that I can return the same 404’s both programatically and by default, so it all looks the same to the end user. This post sat in draft for months. I stumbled upon it again and found great success returning good error messages based on user preferences. the default remains json, but if a user requests text/html it will be an html response, and text for application/rtf or text/plain
This page shows how to customize your fastapi errors. I found this very useful to setup common templates so that I can return the same 404’s both programatically and by default, so it all looks the same to the end user.
This post sat in draft for months. I stumbled upon it again and found great success returning good error messages based on user preferences. the default remains json, but if a user requests text/html it will be an html response, and text for application/rtf or text/plain

Creating SSH Apps with Charm Wish and Laravel Prompts | Joe Ta…
Note Joe has a sick cli.labs site for deploying tui applications.
Joe has a sick cli.labs site for deploying tui applications.
white-space - CSS: Cascading Style Sheets | MDN
Note html can preserve newline \n characters by styling an element with white-space: pre-wrap; pre-wrap Sequences of white space are preserved. Lines are broken at newline characters, at , and as necessary to fill line boxes.
html can preserve newline \n characters by styling an element with white-space: pre-wrap;
pre-wrap Sequences of white space are preserved. Lines are broken at newline characters, at , and as necessary to fill line boxes.
</> htmx ~ The response-targets Extension
Note The htmx response-targets extension allows me to respond to errors from the backend and do normal htmx swaps. Note Load the extension in head Use the extension on an endpoint that might return a 400.
The htmx response-targets extension allows me to respond to errors from the backend and do normal htmx swaps.
Note
Load the extension in head
Use the extension on an endpoint that might return a 400.
How to Restart All Pods in a Kubernetes Namespace | Boot.dev
Note As of kubernetes 1.15 there is an easy way to restart all pods in a deployment. Thanks Lane give him a follow @wagslane
As of kubernetes 1.15 there is an easy way to restart all pods in a deployment.
Thanks Lane give him a follow @wagslane

⭐⭐⭐⭐⭐ Changelog Master Feed
Note Jerod (It’s ya boi) and Adam are my favorite tech news nerds, and have the sickest podcasts in tech. Yes plural podcasts they run seven podcasts maybe more. If you want it short and sweet they got the best 15 minutes of tech news each week this is it. My favorite is Ship it, sad to see Gerhard go, but Justin and Autumn are crushing it. Every episode is highly polished and surrounded by the sickest beats in podcasting. Subscribe to one pod if you want, but I recommend collecting them all with the master feed. ⭐⭐⭐⭐⭐
Jerod (It’s ya boi) and Adam are my favorite tech news nerds, and have the sickest podcasts in tech. Yes plural podcasts they run seven podcasts maybe more. If you want it short and sweet they got the best 15 minutes of tech news each week this is it. My favorite is Ship it, sad to see Gerhard go, but Justin and Autumn are crushing it. Every episode is highly polished and surrounded by the sickest beats in podcasting.
Subscribe to one pod if you want, but I recommend collecting them all with the master feed.
⭐⭐⭐⭐⭐
MarkdownDown
Note Small web app to convert html into markdown. Pretty cool idea. I actually want to look into this for reader and see how well it would work. Right now I am just pulling descriptions, but maybe I can pull full web pages, and keep the full intent of the first 200 words or so in the cards.
Small web app to convert html into markdown. Pretty cool idea. I actually want to look into this for reader and see how well it would work. Right now I am just pulling descriptions, but maybe I can pull full web pages, and keep the full intent of the first 200 words or so in the cards.

Boston Dynamics’ new humanoid moves like no robot you’ve ever …
Note Award for the creepiest way to stand up a robot from lying flat.
Award for the creepiest way to stand up a robot from lying flat.
Rug pull, not cool! (Changelog & Friends #40)
Note Five star episode with Jarod and Adam shootin the crap. The massive Cease and Desist Sucks that the guest had to back out, what a wild world 2024 is. Filled with license and pricing changes. From Vim to Zed Interesting to hear the journey into zed, way to go Thorston diving all the way into working at zed. Boston Dynamics’ new Atlas I later saw this through a YT short, and man does it hold up to the creepy level that they described. MarkdownDown This is a legit cool service, that converts html into markdown
Five star episode with Jarod and Adam shootin the crap.
The massive Cease and Desist
Sucks that the guest had to back out, what a wild world 2024 is. Filled with license and pricing changes.
From Vim to Zed
Interesting to hear the journey into zed, way to go Thorston diving all the way into working at zed.
Boston Dynamics’ new Atlas
I later saw this through a YT short, and man does it hold up to the creepy level that they described.
MarkdownDown
This is a legit cool service, that converts html into markdown
Manual Upgrades | K3s
Note You can give k3s an install channel to install stable, latest, or specific versions like 1.26. This is handy to make sure that you install the same version on all of your workers.
You can give k3s an install channel to install stable, latest, or specific versions like 1.26. This is handy to make sure that you install the same version on all of your workers.
Devin’s Upwork “side hustle” exposed (Changelog News #90)
Note Damn 2024 is such a shit show, now Devin seems to be out as a complete scam. It’s really teaching us to have skepticism for what you find on the internet. Turns out that when broken down frame by frame much of the description in the video was a straight up lie. Personally it seemed quite plausible that it was percentage points better than the competition, but I was not holding my breath for it to be a hands off engineer.
Damn 2024 is such a shit show, now Devin seems to be out as a complete scam. It’s really teaching us to have skepticism for what you find on the internet. Turns out that when broken down frame by frame much of the description in the video was a straight up lie. Personally it seemed quite plausible that it was percentage points better than the competition, but I was not holding my breath for it to be a hands off engineer.
sql - How can I list the tables in a SQLite database file that…
Note I learned about the sqlite_master table from this stack overflow answer. This helps make a lot of sense to how sqlite works. The master table contains all the sqlite objects and the sql to create them. The .tables, and .schema “helper” functions don’t look into ATTACHed databases: they just query the SQLITE_MASTER table for the “main” database. Consequently, if you used
I learned about the sqlite_master table from this stack overflow answer. This helps make a lot of sense to how sqlite works. The master table contains all the sqlite objects and the sql to create them.
The .tables, and .schema “helper” functions don’t look into ATTACHed databases: they just query the SQLITE_MASTER table for the “main” database. Consequently, if you used
inline-snapshot
Note This is a cool snapshot testing tool that automatically creates, and updates test values for you. Starting with some test code. now if I run pytest my tests will fail because my assert will fail, but if I run pytest --inline-snapshot=create it will fill out my snapshot values and the file will then look like this.
This is a cool snapshot testing tool that automatically creates, and updates test values for you.
Starting with some test code.
now if I run pytest my tests will fail because my assert will fail, but if I run pytest --inline-snapshot=create it will fill out my snapshot values and the file will then look like this.
nalgeon/redka: Redis re-implemented with SQLite
Note Redka a sick new redis compatable api, that uses sqlite as its backend datastore. It feels lightweight to use as it is a single small binary. Data does not have to fit into memory as it uses sqlite to store data.
Redka a sick new redis compatable api, that uses sqlite as its backend datastore. It feels lightweight to use as it is a single small binary. Data does not have to fit into memory as it uses sqlite to store data.
Arch Linux - News: The xz package has been backdoored
Note Check your system to see if you are vulnerable to the xz backdoor. I found this line most pertanent to me. The xz packages prior to version 5.6.1-2 (specifically 5.6.0-1 and 5.6.1-1) contain this backdoor. Also it appears that arch is not vulnerable as it does not directly link openssh to liblzma, so the known attack vecotor is not possible. read to the end of the linked article for more.
Check your system to see if you are vulnerable to the xz backdoor.
I found this line most pertanent to me.
The xz packages prior to version 5.6.1-2 (specifically 5.6.0-1 and 5.6.1-1) contain this backdoor.
Also it appears that arch is not vulnerable as it does not directly link openssh to liblzma, so the known attack vecotor is not possible. read to the end of the linked article for more.

From Vim To Zed - YouTube
Note I found this statement quite intriguing. multi-cursors are just macros. This is quite a philisophical video and mostly prime talking about the things that make vim vim, and what prime needs in and editor vs what he can live without.
I found this statement quite intriguing.
multi-cursors are just macros.
This is quite a philisophical video and mostly prime talking about the things that make vim vim, and what prime needs in and editor vs what he can live without.

Use an llm to automagically generate meaningful git commit mes…
Note This is pretty sick, I wanted this early on when I was making lockhart. I wanted to do the git hook thing but could not figure it out and did not know that prepare-commit-msg was a hook that I could use. Git Hooked Then I remembered! Git hooks! Lol. Why would I have that in my brain - who knows! I asked claude again, and they whipped up a simple script that would act as a hook that triggers with the prepare-commit-msg event. This is awesome, cuz if you want to add a git message, you can skip the hook. But if you are lazy, you exclude the message and it will call the LLM. Simon Willison’s llm cli comes in clutch here, it has such a good intereface to allow a prompt to be piped in, but the system prompt be set by -s. I love hacking on projects, but often I am super bad at making commits that make sense. I completely relate to this statement, and this is why I am trying it.
This is pretty sick, I wanted this early on when I was making lockhart. I wanted to do the git hook thing but could not figure it out and did not know that prepare-commit-msg was a hook that I could use.
Git Hooked Then I remembered! Git hooks! Lol. Why would I have that in my brain - who knows!
I asked claude again, and they whipped up a simple script that would act as a hook that triggers with the prepare-commit-msg event.
This is awesome, cuz if you want to add a git message, you can skip the hook. But if you are lazy, you exclude the message and it will call the LLM.
Simon Willison’s llm cli comes in clutch here, it has such a good intereface to allow a prompt to be piped in, but the system prompt be set by -s.
I love hacking on projects, but often I am super bad at making commits that make sense.
I completely relate to this statement, and this is why I am trying it.
node.js - How to fix npm throwing error without sudo - Stack O…
Note Its sad that this is not the accepted answer.
Its sad that this is not the accepted answer.
Note + Pinout for nice!nano boards. Note that P0.15 means gpio port 0 pin 15, they can be referenced in zmk when setting column and row pins.